About
Somesh Motupally
DevSecOps & Cloud Security Engineer
I'm Somesh Motupally, a DevSecOps and cloud security engineer. I work across Harness CI/CD, GitHub Actions, and Azure DevOps — building the guardrails that keep software delivery fast and safe: secret scanning, SAST/SCA, policy-as-code enforcement, and container and Kubernetes hardening.
My focus is the part of security most teams get wrong: not the tools themselves, but getting engineering organizations to actually adopt them. Reusable pipeline templates, self-service guardrails, policy gates that block bad deploys without blocking developers — the unglamorous platform work that decides whether security controls survive contact with production.
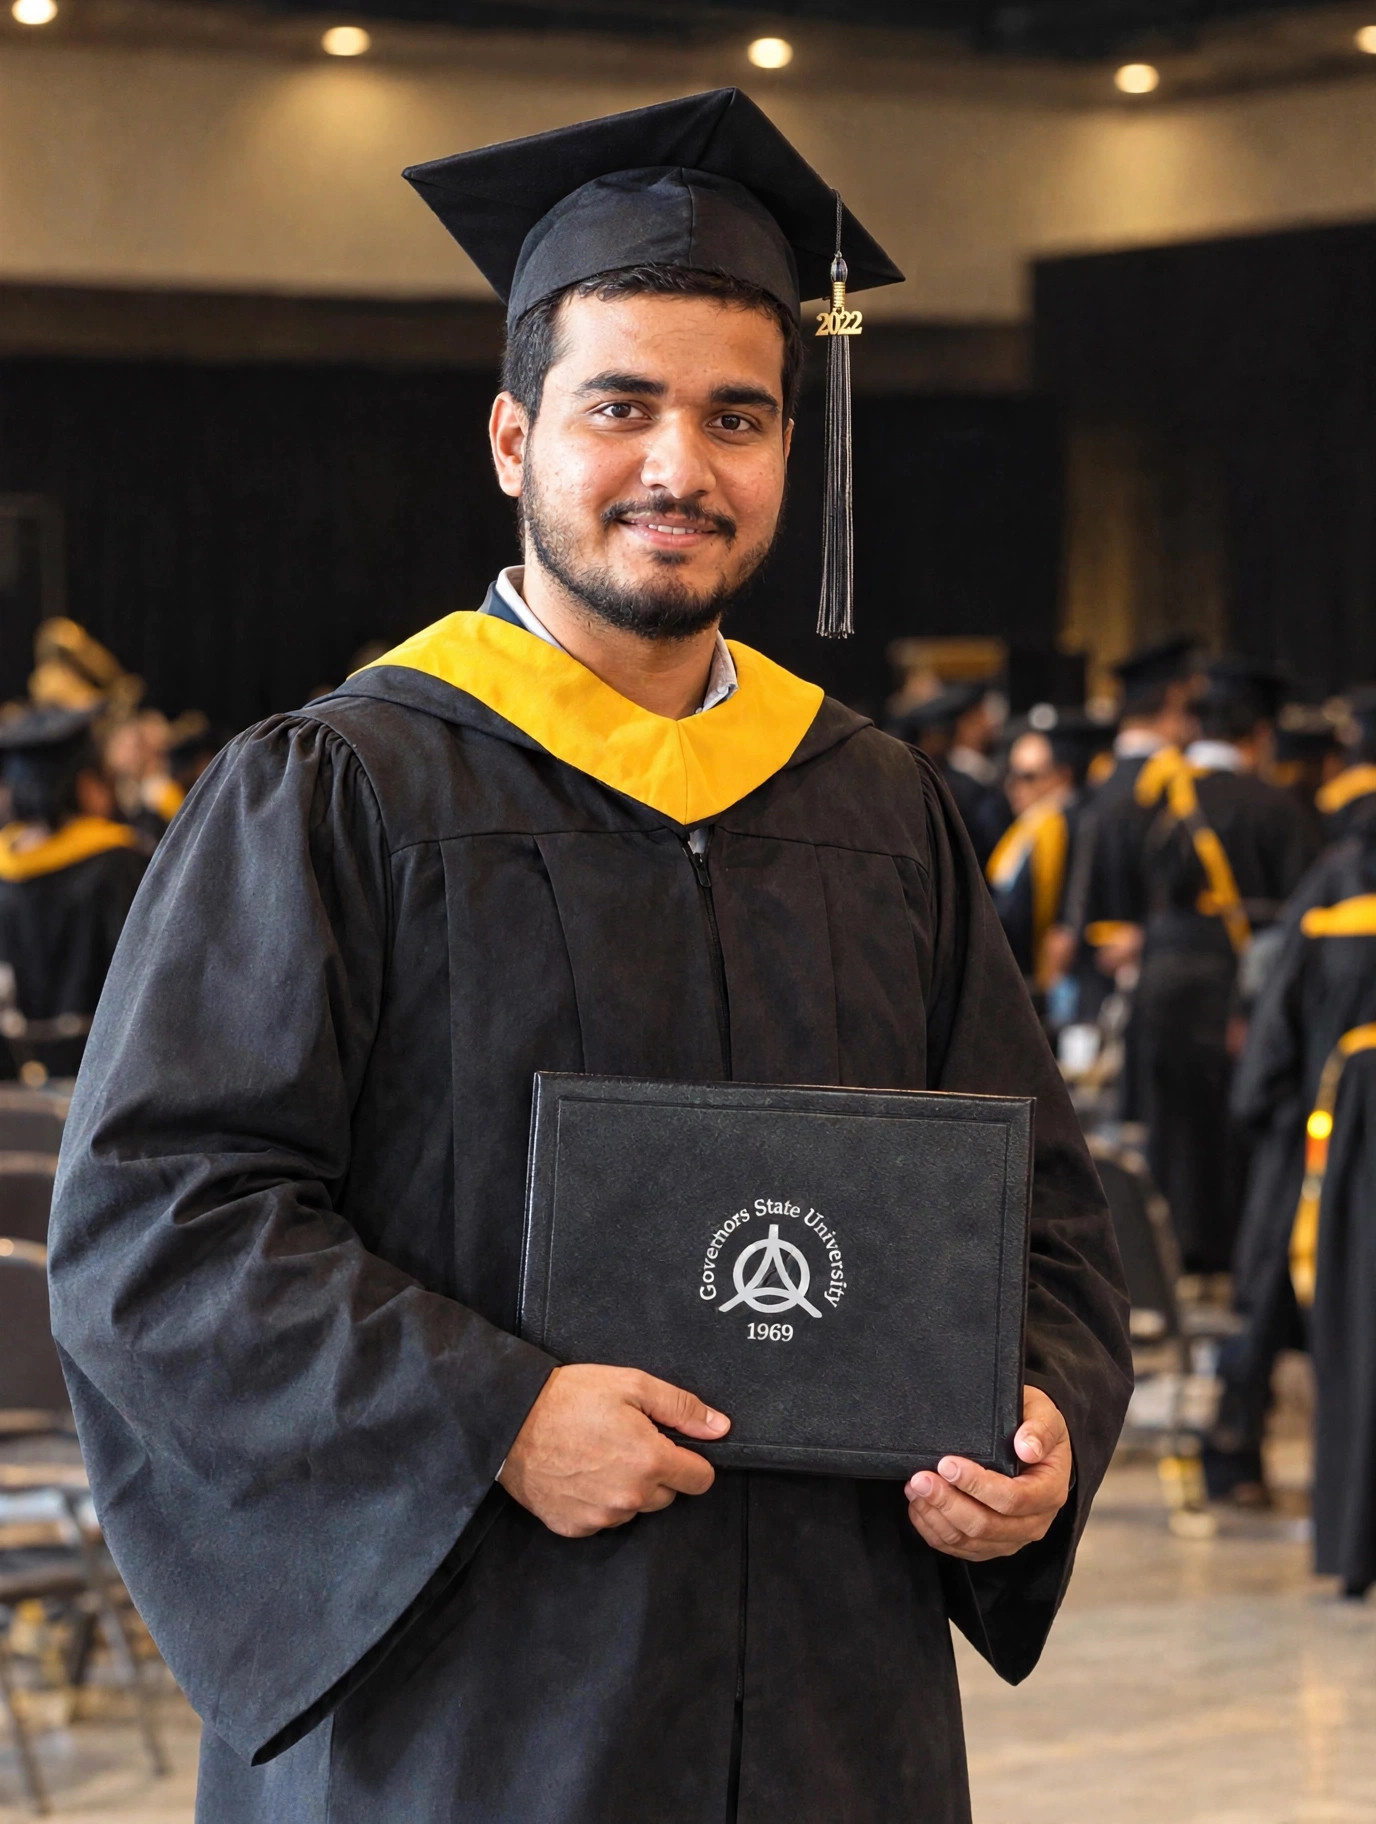
Education
Master of Science in Computer Science
Governors State University — Chicago, IL
Graduated 2022
Why PipelineClear exists
PipelineClear is my working record of that engineering: field notes on building, breaking, and rebuilding security controls in real pipelines. Every post comes from something actually built and shipped — the problem it solved, how it was implemented, what changed as a result, and what didn't work the first time.
No theory, no vendor marketing. Just a public, dated record of hands-on work, written so the next engineer facing the same problem starts further ahead.
What I write about
- CI/CD pipeline security — templates, guardrails, and self-service platforms
- Secret scanning and secrets management
- SAST/SCA and dependency security
- Policy-as-code enforcement (OPA, Kyverno)
- Container and Kubernetes hardening, network policy, workload identity
Get in touch
For questions, collaboration, or speaking and review requests: [email protected] — or connect on LinkedIn.
New notes land every couple of weeks — subscribe via RSS or start with the Pipeline to Runtime series.